Secure every layer of your digital environment.
Cybersecurity solutions
A layered security approach covering network, endpoint, identity, email and cloud.
Security is not only a perimeter question. We cover the network edge, the endpoints behind it, the identities that connect and the mailboxes threats arrive through.
- Layered defence
- Managed detection
- Identity security
- Assessment & VAPT
Overview
Protection that does not stop at the firewall
Organisations need to protect the network perimeter, but also the endpoints, email systems, identities and remote users through which threats actually enter. A control at one layer does not compensate for an absent control at another.
Our cybersecurity solutions span next-generation firewalls, endpoint and workspace protection, detection and response, identity security, email security and independent assessment.
What we provide
Cybersecurity
The components we design, implement and support within this area.
Next-generation firewall
Application-aware inspection, intrusion prevention, threat intelligence and access control, more visibility over what crosses the boundary, and less exposure to what should not.
Endpoint security
Protection on the laptops, desktops and servers themselves, behind the perimeter rather than at it.
Workspace protection
Protection for the collaboration suite itself, covering mail, files and chat, where a large part of the working day now happens.
EDR, endpoint detection and response
Detection and response on the device: behaviour that looks wrong is flagged and can be contained on the endpoint, not merely reported.
XDR, extended detection and response
Detection correlated across endpoints, network, mail and identity, so a chain of small signals is read as one incident.
MDR, managed detection and response
Detection and response delivered as a service, with people reviewing the alerts rather than a console nobody has time to open.
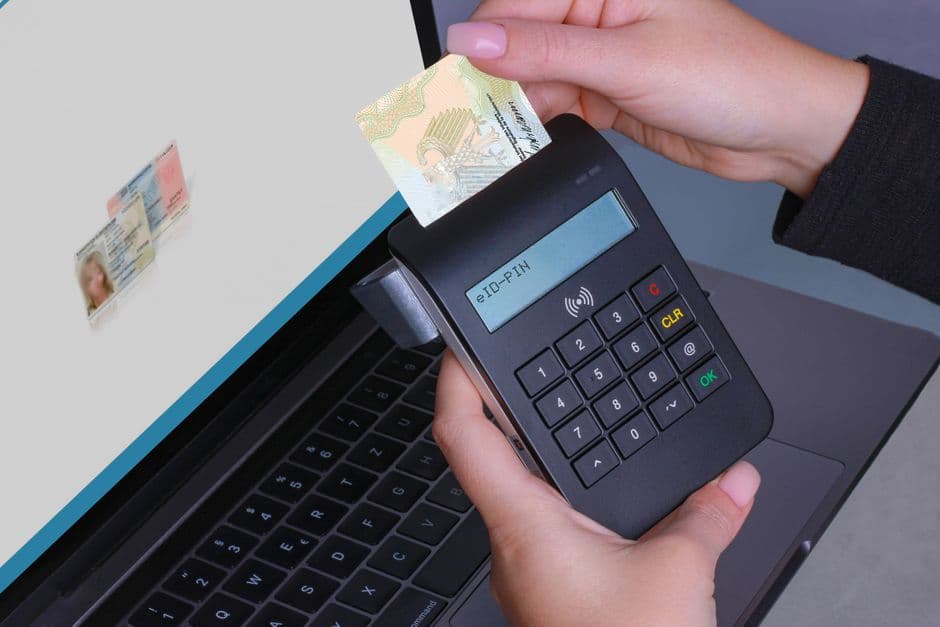
ITDR, identity threat detection and response
Detection aimed at identity attacks specifically, credential misuse, privilege escalation and suspicious sign-in behaviour.
Email security
Filtering and sandboxing for phishing, spam, suspicious links and malicious attachments, before they reach someone who has to judge them.
ZTNA, zero trust network access
Access granted per user and per application rather than by placing someone on the network, so a stolen login reaches less.
NDR, network detection and response
Detection drawn from network traffic itself, which sees activity that never touches a managed endpoint.
DNS protection
Filtering at the name-resolution layer, so known-bad destinations fail to resolve before a connection is ever made.
SOC, security operations centre
The people and tooling that watch security telemetry continuously and decide what actually warrants action.
SIEM, security information and event management
Central collection and correlation of logs from across the estate, so events can be searched, alerted on and reconstructed in one place.
Network security
Segmentation, inspection and access rules at the network layer, limiting what is able to reach what.
Secure remote access
VPN and remote-access solutions giving authorised users secure connectivity to business infrastructure from wherever they work.
Identity security
Protection for accounts and privileges: multi-factor enforcement, conditional access, and review of who can reach what.
Security assessment
A structured review that identifies weaknesses and gaps, and produces a documented findings report usable in compliance reviews and vendor security assessments.
VAPT
Vulnerability assessment identifies known weaknesses; penetration testing actively attempts to exploit them. Together they give a fuller picture than either alone.
Our approach
From discovery to ongoing support
The same seven steps on a single office and a multi-site rollout. Only the scale changes.
- 01Discover
Understand your business, users, locations, applications and operational requirements.
- 02Assess
Evaluate existing infrastructure, identify limitations and establish technical requirements.
- 03Design
Develop the appropriate architecture, technology stack and implementation approach.
- 04Deploy
Execute implementation with structured project management and minimal operational disruption.
- 05Validate
Test, commission and verify the deployed environment.
- 06Document
Deliver relevant configuration, infrastructure and project documentation.
- 07Manage
Provide ongoing support, maintenance and optimisation.
What your organisation gains
- Reduced attack surface
- Better security visibility
- Secure remote access for distributed teams
- Layered protection across network, endpoint and identity
- Documented evidence for compliance requirements
- Faster detection and response
Planning Cybersecurity work?
Not sure where your exposure is? Start with an assessment and a documented set of findings you can act on.